Authorization
Regulatory fit as a payment institution
"Before opening the application file, you need to confirm whether your model really fits as a payment institution and which services you will provide. That decision shapes everything else."
We structure your project and defend your payment institution license application before the Bank of Spain: regulatory fit analysis, programme of operations, complete application file, safeguarding of funds, AML/CFT, corporate governance and ongoing compliance.
Need a PI license? Free assessment
Tell us about your business model and we will tell you whether you fit as a PI, an EMI or a PISP/AISP before the Bank of Spain.
Quick answer
A payment institution (PI) license in Spain is the Bank of Spain authorization to provide payment services on a professional basis under PSD2 and Royal Decree-law 19/2018. It requires initial capital of €20,000 to €125,000 depending on the services, safeguarding of client funds and a complete application file with a programme of operations. The statutory deadline for a decision is 3 months; in practice, it takes 6 to 12 months.
Six building blocks that make up a solid, consistent and defensible application file before the Bank of Spain.
We analyze whether your model needs to apply for a PI license, whether it fits another financial license type (EMI, PISP, AISP) or whether it needs a different contractual structure before you start operating.
We prepare the key documents of the application file: programme of operations, policies, annexes, functions, evidence and responses to information requests, for a stronger application process.
We design an organization you can defend: directors, key functions, segregation of duties, reporting and a proportionate risk map.
We review the flow of funds, reconciliations, incidents, critical providers and safeguarding measures so the model withstands real supervision.
We implement the anti-money laundering framework: risk assessment, onboarding, monitoring, training, reporting and operational evidence.
We organize outsourcing, SLAs, business continuity and DORA compliance so the license works in practice, not just on paper.
Payment platforms, fintechs with wallets, PISP/AISP models or operators that want their own license: every project has its own regulatory fit and its own specific requirements.
"Before opening the application file, you need to confirm whether your model really fits as a payment institution and which services you will provide. That decision shapes everything else."
"You don't win a payment institution license with nice-looking documents: you need consistency between business, governance, policies, technology, third parties and evidence."
"The operating structure has to hold up in practice: funds, reconciliations, incidents, customer service, critical providers and controls that stand up to review."
"Authorization is not the finish line. A payment institution needs working AML/KYC, internal control, reporting, training and constant monitoring from day one."
Operating without a license, filing an inconsistent application or improvising ongoing compliance can block your operations, your fundraising and your banking relationships.
The most common mistake: launching a payment solution without first working out whether the activity requires a license. The problem surfaces once the product is already built, and the cost of fixing it soars.
The Bank of Spain reviews consistency, not just documents: if the business, policies, governance, AML/KYC and outsourcing do not fit together, the application loses strength and information requests multiply.
Safeguarding and internal control cannot be left until the end: they are central to making the license defensible and to letting the institution scale safely.
Providing payment services without prior authorization can lead to the immediate shutdown of the activity.
Fines and personal liability for directors for providing financial services without a license.
Banks and financial partners require an active license before integrating a fintech into their ecosystem: without one, deals stall indefinitely.
Before opening the application file, it pays to validate the regulatory perimeter, put the business in order and check whether your structure can meet the requirements for authorization, safeguarding, AML/CFT and ongoing control.
The payment institution license is the authorization to provide certain payment services on a professional basis within the regulatory framework that applies in Spain. It is not a banking license or an EMI license: it has its own regulatory perimeter.
The key is not just obtaining the license, but being able to run an institution that can be supervised from day one: controls in operation, funds safeguarded and compliance that is actually alive.
When the model enters the chain of payment execution, order handling or operations with client funds, and can no longer be presented as a purely technological or ancillary activity.
The usual mistake is to assume that having a software layer means there is no regulated activity. That misunderstanding tends to break the project when partners, product and investment are already committed.
Each license type has a different regulatory perimeter and its own requirements depending on the service you want to provide:
Choosing the wrong license type from the outset delays the whole process and may force you to restructure your business model.
It reviews whether the application file is consistent, complete and defensible: programme of operations, corporate structure, directors, key functions, internal policies, control system, third parties, technology and real capacity to operate.
The supervisor checks whether the business described can be sustained by people, processes, contracts, controls and evidence that make sense together. Document consistency matters as much as the legal content.
Safeguarding of funds and the AML/CFT framework are two central pieces of a payment institution, not secondary annexes. They affect the quality of the application, the relationship with banking partners and the future strength of the institution.
They force you to set out in practice the flow of funds, reconciliations, onboarding, monitoring, reporting, internal roles and evidence. When they are improvised, the supervisor spots it quickly.
The statutory deadline for a decision is 3 months from the filing of the complete application, although in practice the process can stretch to 6-12 months depending on the complexity of the model and the quality of the application file.
What usually makes a license more expensive and slower is not drafting it, but fixing it: redoing annexes, clarifying contradictions, answering information requests or redesigning parts of the business that had not been properly closed.
As a general rule, no. Providing payment services without prior authorization is a very serious infringement.
There are some limited exceptions (an exemption regime for very small volumes, ancillary activities) that must be analyzed case by case. The usual alternative while your own license is being processed is to operate under the umbrella of an already authorized institution through an agent or regulated distribution agreement.
The most important phase begins: operating as a supervised institution with ongoing compliance, internal control, incident follow-up, third-party oversight, training and reporting.
The license is not the end of the project: it is the starting point of supervised operations.
There is no single figure: the cost varies with the model, the range of services and the project's starting point. The factors that drive the cost are:
What stretches out the process and drives up the cost is not drafting the application file, but fixing it: a regulatory fit that was poorly defined at the start costs months and extra rounds of information requests.
It depends on the actual flow of funds. If the platform:
The usual mistake is to assume that using Stripe, Adyen or another provider means you carry out no regulated activity of your own. The reality depends on the contractual and technical design of the flow, not on the tools you use.
Each option makes sense at a different stage:
Many projects start as an agent and, once the model is validated, apply for their own license. The transition must be planned well in advance, because changing the regulatory status affects clients, contracts and operations.
The PI license application file includes, among other documents:
The quality and consistency across these documents carries as much weight as the correctness of each one on its own.
As of July 2026, PSD3 and the PSR Regulation are still going through the EU legislative process and do not yet apply: your license is governed by PSD2 (Royal Decree-law 19/2018). Once adopted, the reform is expected to fold EMIs into the payment institution category, tighten anti-fraud controls (payee verification, SCA) and open a transitional re-authorization period for institutions that are already licensed.
In practice: don't wait for PSD3 to apply for your license — obtaining it now with a solid application file gives you an edge in the transition — but design your policies and technology with the new requirements in mind.
Catalog of payment services in Article 1.2 of Royal Decree-law 19/2018 (which replaced Law 16/2009). If your model fits any of these services, the activity is regulated and you need a payment services license from the Bank of Spain.
Services enabling cash to be placed on a payment account, and all the operations required to operate that account.
Services enabling cash to be withdrawn from a payment account, and all the operations required to operate it.
Direct debits, card payments and credit transfers, including those carried out through a credit line.
The same transactions as in point 3 where the funds are covered by a credit line granted to the user.
Issuing and acquiring of payment instruments (cards, devices, credentials) by authorized providers.
Transactions in which funds are received without opening a payment account, for the sole purpose of transferring them to a payee.
Initiating a payment order at the user's request in respect of an account held with another payment service provider.
Online services that provide consolidated information on the user's payment accounts held with other providers.
Does your product fit any of these? You very likely need a PI license, an EMI license or a PISP authorization or an AISP registration. Download the free checklist or request an assessment.
The four regulated license types that are most often confused, side by side: minimum capital, client funds, complexity of the application file and real timelines.
| Feature | Payment institution (PI) | EMI (electronic money) | PISP / AISP | Bank |
|---|---|---|---|---|
| Minimum capital | €20,000 – €125,000 | €350,000 | €50,000 (PISP) / No minimum (AISP, professional indemnity insurance required) | €5,000,000 |
| Client funds | Receives and executes payments (with safeguarding) | Receives, stores (electronic money) and executes payments | Does not handle client funds | Takes deposits and provides financial services |
| Typical services | Transfers, direct debits, card payments, remittances | Wallets, prepaid cards, stored balances, e-wallets | Payment initiation (PISP) / Account aggregation (AISP) | Deposits, lending, mortgages, corporate banking |
| Safeguarding of funds | Mandatory (segregated accounts or insurance) | Mandatory (segregated accounts or insurance) | Not applicable (no client funds held) | Subject to the banking prudential regime |
| DORA applies | Yes (since January 2025) | Yes (since January 2025) | Yes (since January 2025) | Yes (since January 2025) |
| Average real timeline | 6 – 12 months | 9 – 15 months | 3 – 6 months | 18 – 36 months |
| Supervision | Bank of Spain | Bank of Spain | Bank of Spain (registration) | Bank of Spain / ECB (SSM) |
| EU passport | Yes (notification to the host regulator) | Yes (notification to the host regulator) | Yes (notification to the host regulator) | Yes (notification to the host regulator) |
| Typical business model | Processors, remittance companies, B2B platforms, marketplaces with a flow of funds | Neobanks, wallets, prepaid cards, platform e-wallets | Payment initiation apps, financial aggregators, PFM, scoring | Universal or digital banking that takes deposits |
Indicative figures based on Royal Decree-law 19/2018, Law 21/2011 on electronic money and the applicable banking regulations. Each case requires an individual analysis of the perimeter and the specific services to be provided.
Six common fintech business models and the license type that usually fits them. The final decision depends on the actual flow of funds and the specific services provided.
Receives funds in Spain for payees abroad. No issuing of electronic money.
A marketplace that collects from buyers and pays out to sellers, keeping its own commission. If it holds funds, it falls within the regulated perimeter.
Balance stored on the user's behalf, top-ups, prepaid card payments. It involves issuing electronic money.
Virtual accounts for businesses with their own IBANs, management of collections and payments, automated reconciliation.
An app that connects the user's bank accounts to show balances, spending or scoring. It does not handle client funds.
A solution that initiates transfers from the user's account to a payee, without going through a card.
Can't find your model here? Tell us about your project and we will tell you exactly which license type you need and why.
There is no single price. The total cost depends on five factors and, above all, on the range of services you ask to have authorized. Below we break them down and give you a calculator to estimate your statutory minimum capital.
Under Royal Decree-law 19/2018, depending on the payment services to be provided. It is the only item for which the regulator sets an exact numerical minimum.
Regulatory fit, drafting of the application file, internal policies, handling of information requests and operational support throughout the process before the Bank of Spain.
Fit and proper directors, compliance officer, AML/internal control body (OCI), internal audit and risk. They can be in-house staff or outsourced to a qualified provider.
Banking agreements for safeguarding, KYC/AML systems, transaction monitoring, DORA framework, payment infrastructure and cybersecurity.
Periodic reporting, audits, team training, adapting to regulatory changes (PSD3, AMLR) and active handling of the supervisor's information requests.
Starting the application file without having properly settled the license type is the main cause of cost overruns: redoing annexes, answering information requests and redesigning the business.
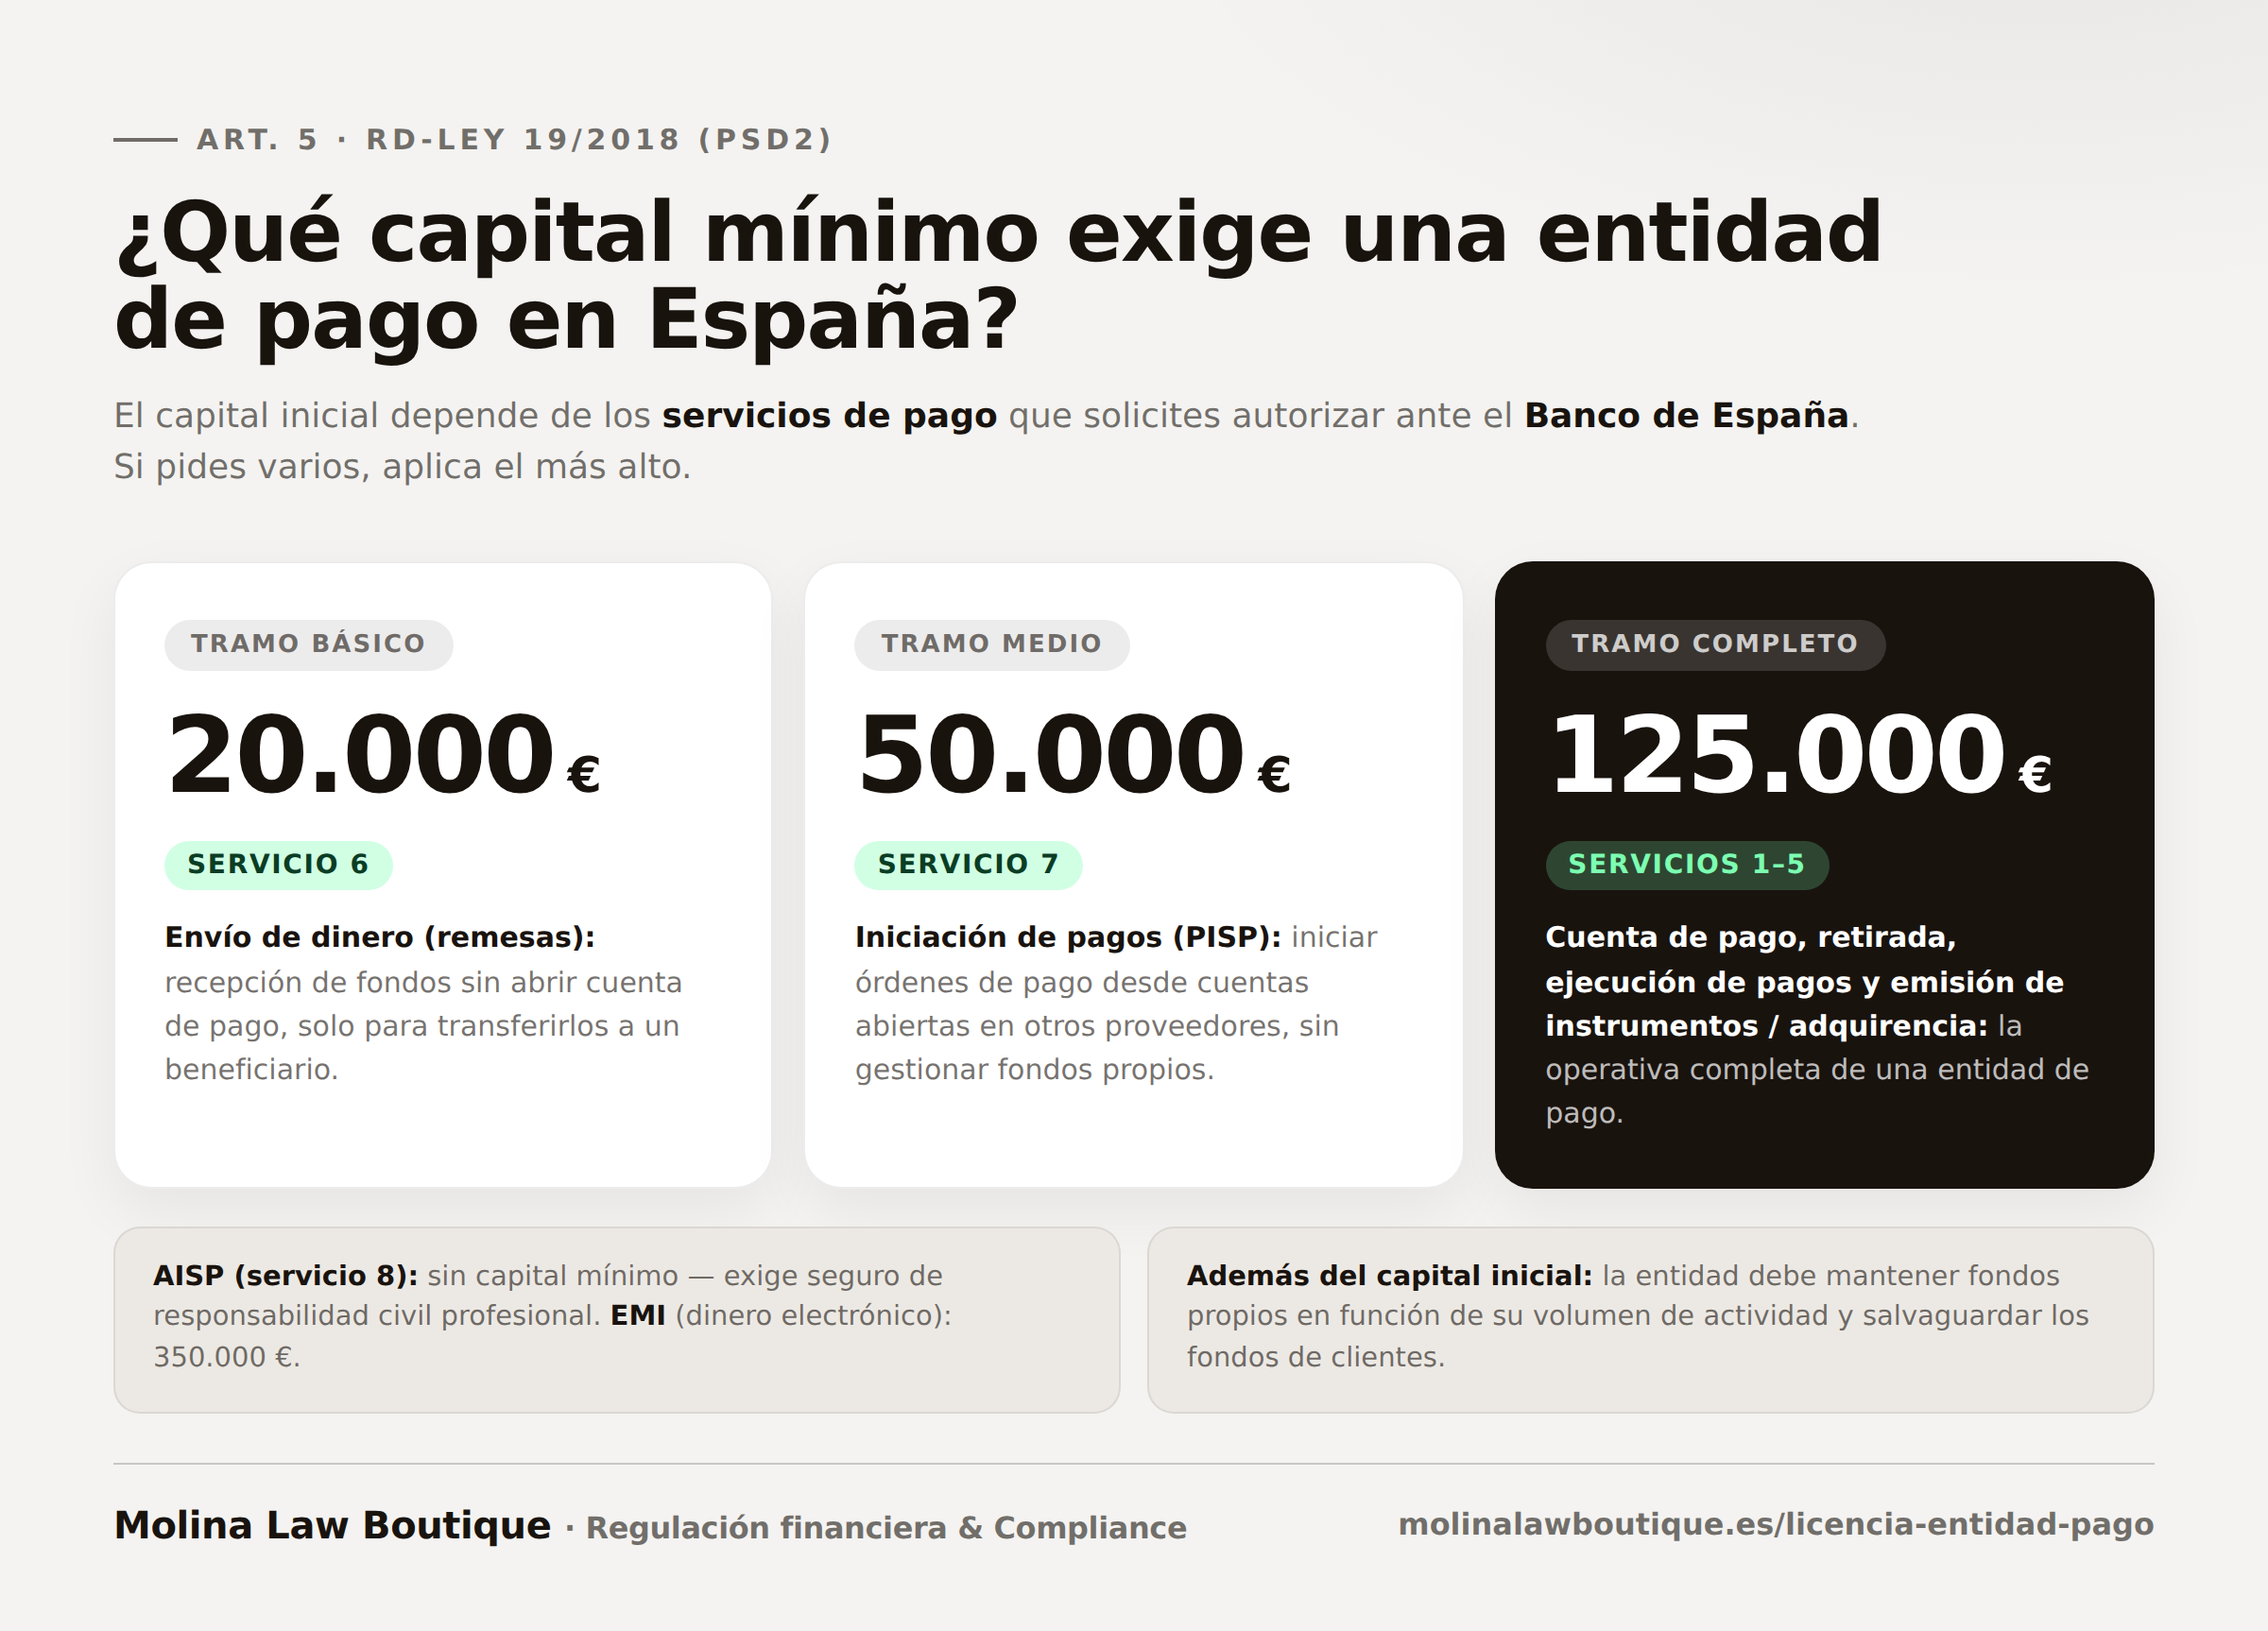
A PI license is not just a formality: it is a system that must show consistency between business model, operations, controls and evidence. The key is to build, from the start, an institution that can withstand real supervision.
The Bank of Spain does not just review the business idea. It analyzes whether the structure can sustain it: fit and proper directors, key functions, consistent policies, workable controls and evidence of real operational capacity.
The flow of funds, reconciliations, account segregation and incident management must be designed before the application file, not as an appendix. A failure here blocks authorization.
Working AML/KYC, DORA, reporting, audits and handling of the supervisor's information requests must be designed to last over time, not just to get the initial application through.
If you want to structure your application file from scratch or review where your project stands, see our fintech regulation services or our dedicated fintech compliance practice.
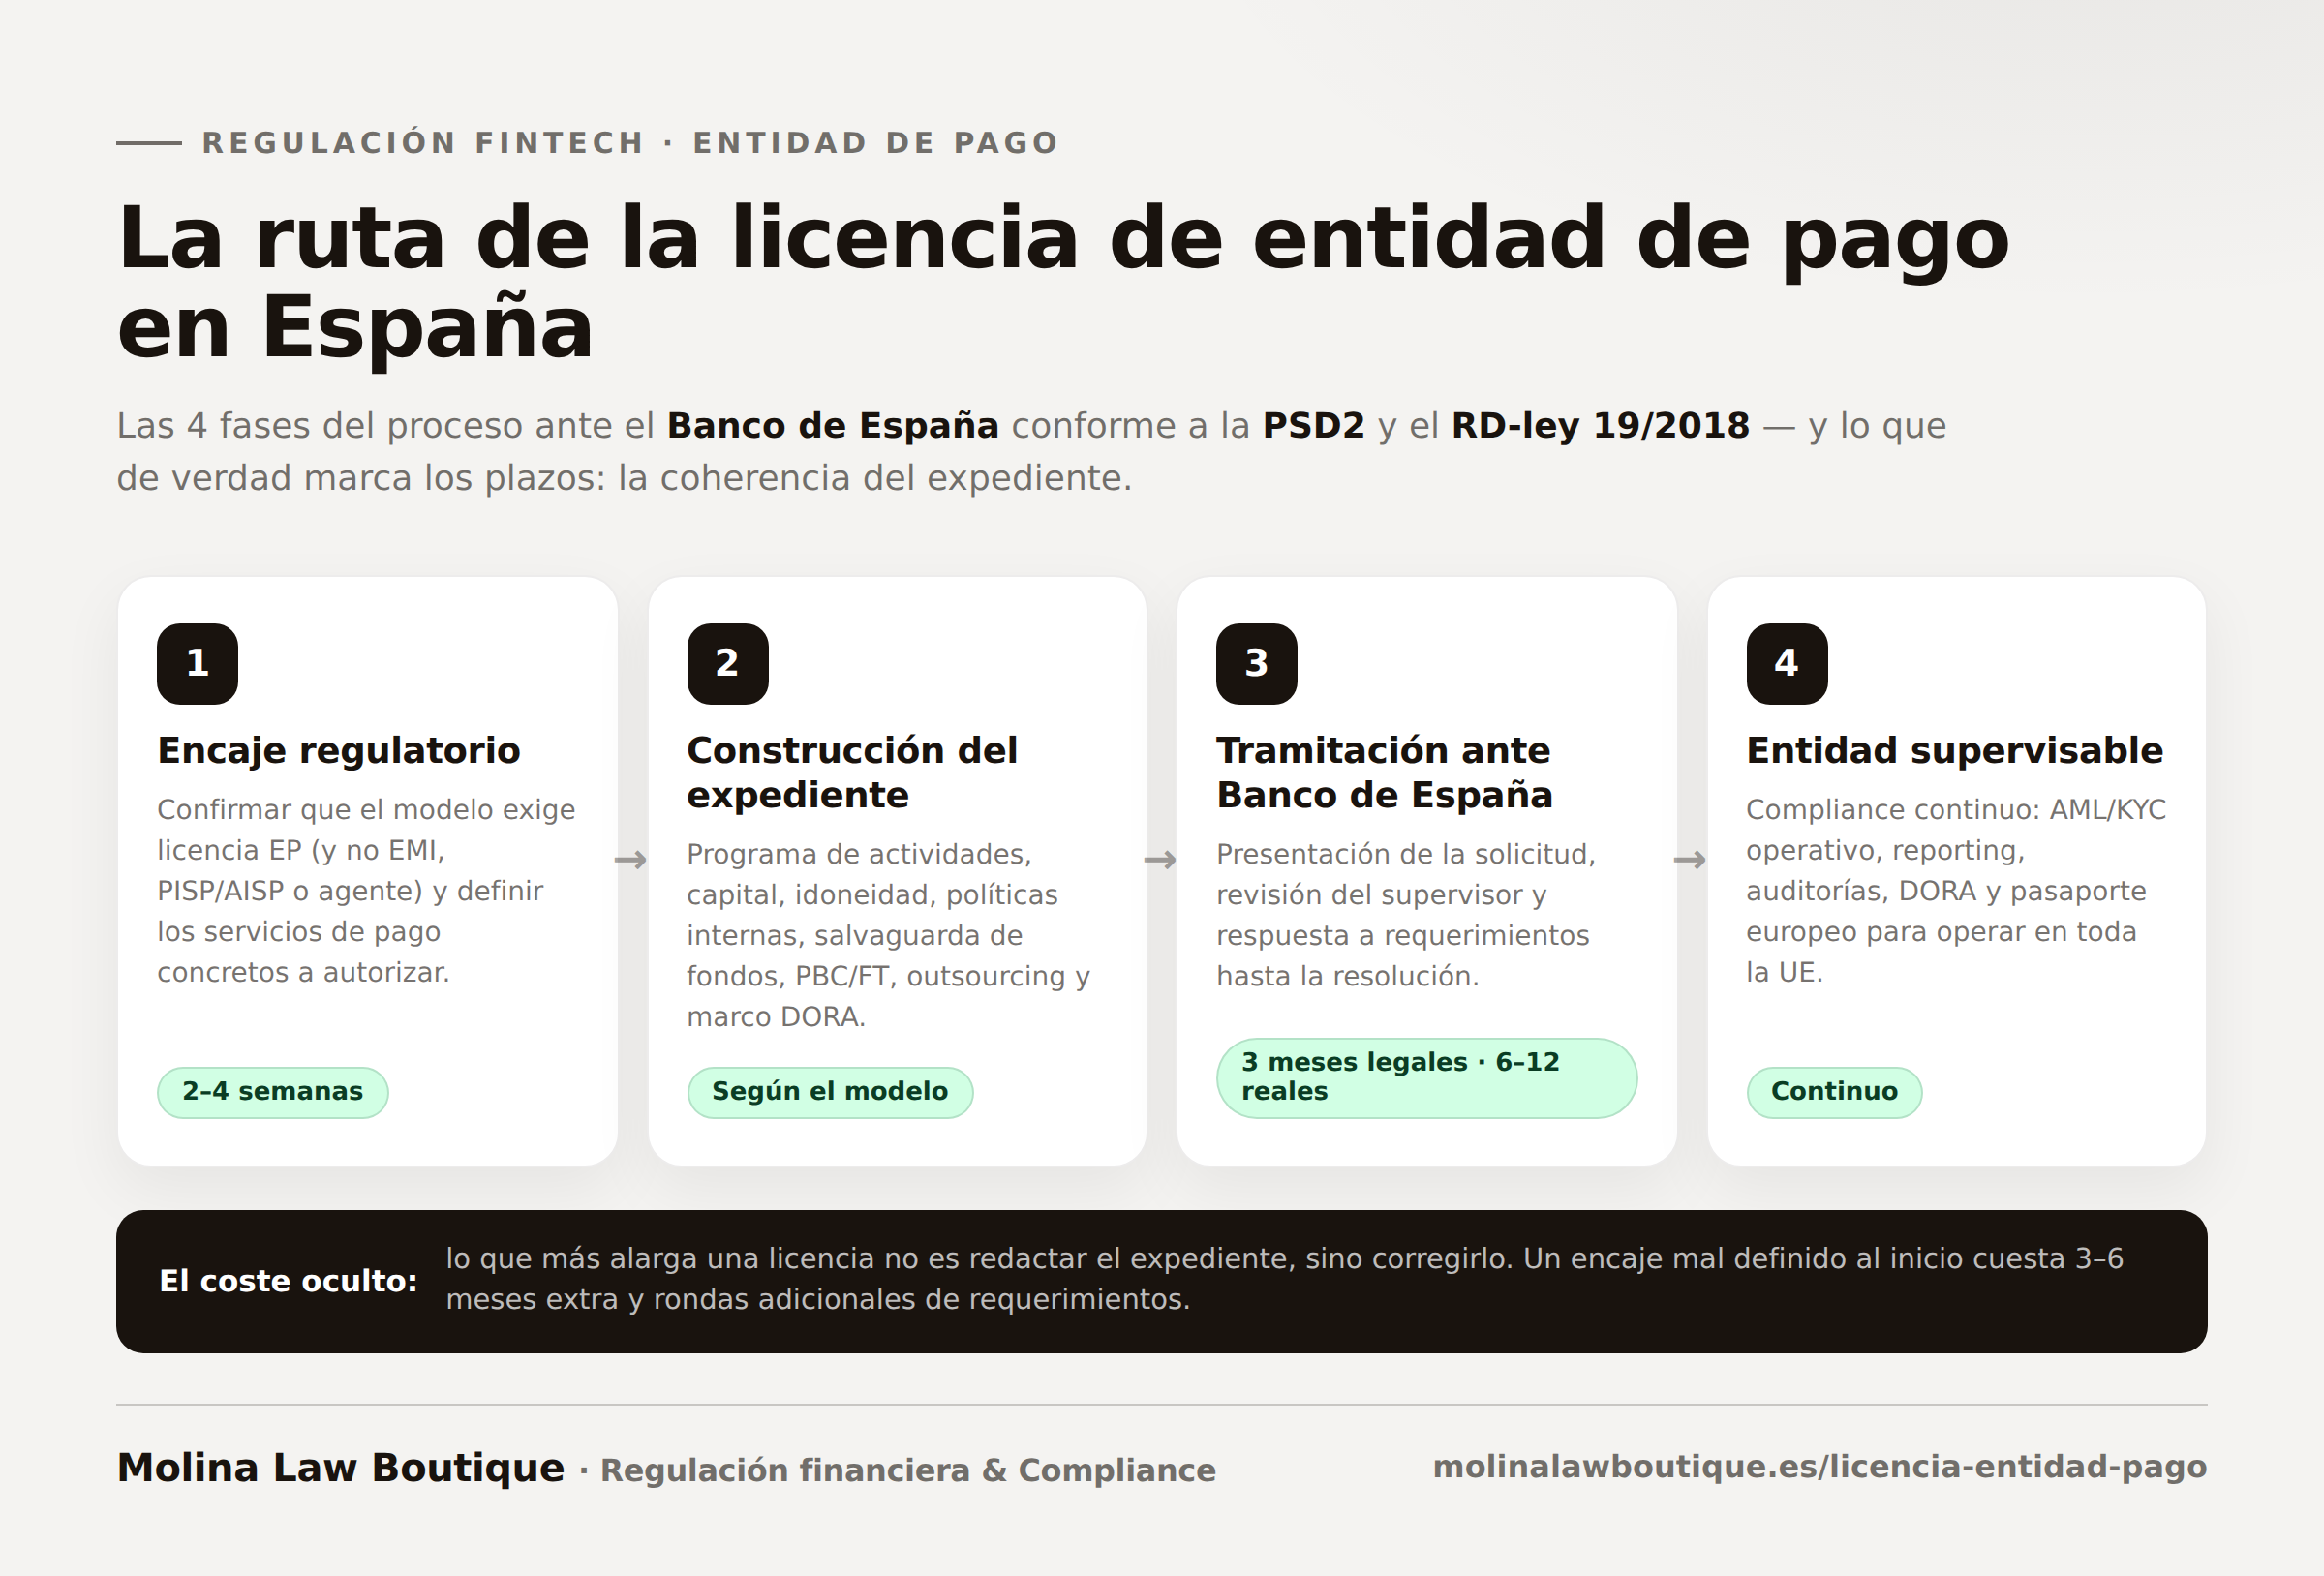
An effective payment institution license is not a dossier: it is a set of consistent decisions (regulatory fit, safeguarding, AML/KYC, governance and outsourcing) backed by traceable evidence. Here is a visual overview of how it works in practice.
 1) Fit
The goal is not to "get the license faster": it is to make sure the model needs one, of which type and with what perimeter. That decision shapes the entire application file.
 2) Application
The supervisor checks consistency. Programme of operations, policies, governance, technology and outsourcing must fit together without internal contradictions.
 3) Safeguarding
Flow of funds, segregated accounts, reconciliations and incidents. When it is designed late, it blocks authorization or creates structural gaps after the license is granted.
 4) Compliance
Working AML/KYC, DORA, audits and reporting turn the PI into a real institution: follow-up, corrections and live evidence from the first day of operation.
 Quick decision
PI license: transfers, direct debits, card payments or remittances without issuing electronic money.
EMI license: you issue electronic money (stored balance, prepaid card). Higher capital requirements.
PISP authorization / AISP registration: you initiate payments or aggregate bank accounts without handling client funds.
A reasoned analysis showing that the actual activity requires a PI license and not another license type (EMI, PISP, unregulated activity).
Regulatory fit report, description of the actual service and comparison of license types.
A consistent description of the business, clients, channels, technology and partners that supports the supervisor's review.
Detailed business report, projections, third-party contracts and functional organization chart.
A clear flow of client funds, segregated accounts, reconciliations and properly handled incidents.
Safeguarding policy, description of the flow of funds, banking agreements and reconciliation procedures.
Risk assessment, onboarding, monitoring and reporting proportionate to the business's risk profile.
AML/CFT manual, KYC files, alert log and evidence of staff training.
Fit and proper directors, key functions, segregation of responsibilities and an internal control system.
Minutes, appointments, conflicts of interest policy, risk map and annual audit plan.
Spot them before filing the application to avoid costly information requests.
The EU is revising the payments framework: the PSD3 directive and the Payment Services Regulation (PSR). As of July 2026 they do not yet apply — your license is governed by PSD2 — but it makes sense to design your application file today with them in mind.
The proposal brings electronic money institutions in as a category within payment institutions. If you are torn between a PI and an EMI today, the line will become thinner: decide your regulatory fit with that convergence in mind.
Payee verification (confirmation of the account holder), stronger authentication (SCA) and new liability rules for fraud. The monitoring you design today will need to absorb these controls.
Institutions already authorized under PSD2 will have a transitional period to adapt to the new framework. Obtaining the license now with a solid application file gives you an edge in that transition.
Status as of July 2026: PSD3 and the PSR are still going through the legislative process in the Council and the European Parliament, with no final application date. We track each milestone and update this page as things progress.
The statutory deadline is 3 months, but most applications stretch to 6-12 because of the same recurring mistakes. These are the ones we see most often and how to avoid them.
The project applies for a PI license when it actually needs an EMI license (because it issues electronic money), or applies for both services when one would do. Result: oversized capital, a reopened application file and months lost.
The application file describes a business that does not match what the tech team is building. The Bank of Spain detects contradictions between the programme of operations, the architecture and the contracts.
The flow of funds is written up at the end, with no signed banking agreements and no detailed reconciliation procedure. It is the #1 cause of blocked payment authorizations.
The proposed directors are brilliant in technology but lack financial experience or real availability. The Bank of Spain requires good repute, experience and genuine time commitment.
Critical technology providers are engaged on a standard SaaS MSA. DORA requires specific clauses, audit rights, an exit plan and a register of critical providers.
A standard AML manual is submitted with no business-specific risk assessment, no tailoring to the actual type of client, and no formal appointment of the internal control body (OCI) or SEPBLAC representative.
One of the big strategic advantages of getting licensed in Spain: the European passport lets you provide payment services in all 27 EU countries without applying for additional authorizations.
Under the PSD2 Directive, payment institutions authorized in any EU Member State can operate in the others through the freedom to provide services or the freedom of establishment (opening a branch or using agents).
The process is a notification to the Bank of Spain, which passes it on to the regulator of the host country. It is not a second authorization: if your license is solid in Spain, it is solid across the EU.
All 27 Member States + the European Economic Area (Norway, Iceland, Liechtenstein) under the EEA arrangements.
A boutique firm specialized in financial regulation. We work exclusively with projects that need Bank of Spain licenses and regulatory compliance: that focus is what makes the difference.
Payment fintechs, EMIs, PISPs/AISPs, AML obliged entities and financial institutions. We know the Bank of Spain's real criteria, not just the theory.
We are not a generalist firm with a fintech department: financial regulation is all we do. That lets us move faster and get straight to the point.
We answer queries in under 24 hours and work side by side with the client's team. No gatekeepers and no juniors reviewing case law: you deal directly with the lawyer in charge.
We support you from the initial assessment through to post-authorization reporting: regulatory fit, application file, handling of information requests, AML, DORA and ongoing compliance.
If you are structuring a PI license, these terms come up in the application file, in internal policies and in your dealings with the supervisor. Understanding them well helps you build a consistent project.
An institution authorized to provide payment services on a professional basis: transfers, direct debits, remittances, card payments or payment initiation.
It can issue electronic money (wallets, prepaid cards, stored balances) in addition to providing payment services. Higher minimum capital than a PI.
The obligation to keep client funds segregated and protected in case the institution becomes insolvent. A central piece of the application file.
The European framework that regulates payment services and sets obligations on SCA, access to accounts (open banking), reporting and transparency of information.
PSD2 license types for operating in open banking: the PISP initiates payments from accounts held elsewhere and the AISP aggregates banking information, without handling client funds.
EU regulation applicable since January 2025 that requires an ICT risk management framework, business continuity, incident reporting and oversight of critical providers.
The core document of the application file: it describes the services to be provided, the business model, the operating structure, the clients and the partners of the future institution.
The heads of compliance, internal audit, risk and AML/CFT, who must be identified, be fit and proper and have real capacity to perform their role.
Technology or essential service providers must be documented: contracts, SLAs, security, continuity and an exit plan for contingencies.
Strong Customer Authentication required by PSD2: at least two independent factors (knowledge, possession, inherence) for electronic payments and online account access.
A single euro payments area that standardizes credit transfers and direct debits across 36 European countries. SEPA Credit Transfer (SCT), SEPA Instant Payments (SCT Inst) and SEPA Direct Debit (SDD).
The OCI (internal control body) is the internal body responsible for AML/CFT compliance. A representative before SEPBLAC, Spain's Financial Intelligence Unit and anti-money laundering authority, must be appointed.
The practical guide we use with our clients to prepare a solid, defensible application file before the Bank of Spain: regulatory fit, capital, programme of operations, governance, safeguarding, AML/CFT, DORA and ongoing compliance.
The laws, authorities and public registers that govern the activity of payment institutions in Spain and the EU. Keep them at hand throughout the process.
Consolidated text of the Royal Decree-law on payment services and other urgent financial measures. It transposes PSD2 into Spanish law.
View on BOE EUR-Lex — European UnionEU directive on payment services in the internal market. A common regulatory framework for payment institutions, strong customer authentication and open banking.
View on EUR-Lex Bank of SpainPublic register of every payment institution authorized in Spain. Useful for checking institutions, agents and providers before doing business with them.
View register EBA — European Banking AuthorityEBA regulatory technical standards (RTS) and guidelines on PSD2: SCA, incident management, outsourcing and communication between providers.
View EBA Payment Services EUR-Lex — European UnionDigital Operational Resilience Act. Applicable since January 2025 to all PIs, EMIs and financial entities in the EU. ICT risk management, business continuity and critical third parties.
View the DORA Regulation SEPBLAC — Spain's Financial Intelligence UnitThe Spanish authority responsible for preventing money laundering and terrorist financing. It receives reports from the internal control body (OCI).
View SEPBLACPayment institutions in Spain are mainly governed by Royal Decree-law 19/2018 of 23 November on payment services and other urgent financial measures, which transposes Directive (EU) 2015/2366 (PSD2). Authorization and supervision are the responsibility of the Bank of Spain, which assesses the suitability of the project, the governance structure, the strength of the application file and the real operational capacity of the future institution.
The services that require a PI license include: services enabling cash to be placed on an account, cash withdrawal services, execution of payment transactions (credit transfers, direct debits, card payments), issuing of payment instruments, money remittance and payment initiation services (PISP). Providing any of these services without prior authorization is a very serious infringement.
The required minimum capital ranges from €20,000 to €125,000 depending on the payment services to be provided. In addition, the institution must maintain sufficient own funds in line with its volume of activity. The application file must include a programme of operations, internal policies, a governance structure with properly accredited key functions and an internal control system proportionate to the risk.
One of the most critical obligations of a payment institution is the safeguarding of users' funds: they must be held in segregated accounts at credit institutions or invested in secure, liquid assets. Compliance with this obligation is directly supervised, and a breach can lead to immediate interim measures.
Since January 2025, the DORA Regulation has applied to all payment institutions authorized in the EU. It requires an ICT risk management framework, a business continuity policy, incident logging and reporting, digital resilience testing and oversight of critical technology providers. PIs that have not adapted their ICT risk management system are exposed to supervisory measures.